Praman by MetricVibes
DPDP compliance, proven
Audit what you already run. Fix what is missing. Keep the proof in one place. Your customers' personal data never leaves your systems.
The clock is running
Full DPDP obligations apply from 13 May 2027
Why now
The timeline, and what's at stake
Penalties are the maximums per instance in the Schedule to the DPDP Act, 2023.
13 Nov 2025
Rules notified. Data Protection Board and administrative provisions in force.
Nov 2026
Registration of Consent Managers begins.
13 May 2027
Everything else: notice, consent, security, breach reporting, retention, rights, grievance and SDF duties.
₹250 cr
Failure to take reasonable security safeguards
₹200 cr
Failure to notify a personal data breach
72 hrs
Detailed breach report to the Board
90 days
Maximum time to answer rights requests
Not legal advice.
What we see in enterprises
Most teams can't yet prove where they stand
No single view
Personal data sits across the CRM, core systems, HRMS, warehouse and a long list of vendors. Nobody has the full map.
Policy ≠ practice
Policies exist, but consent flows, withdrawal, retention jobs and breach playbooks often don't match what's written.
No evidence trail
When the Board or an auditor asks for proof, it lives in inboxes, screenshots and people's memory.
Checklists don't fix things
Gap reports land on a desk. Nobody owns the fix, there's no due date, and nothing is ever re-tested.
Tools want your data
Many compliance tools copy customer data into yet another platform, which adds risk instead of reducing it.
Software can't judge context
Automation flags missing fields. Deciding whether a gap matters for your business still takes an expert.
Our approach
We audit and help you implement. You keep your data
Praman works with configuration, metadata, policies, hashes and evidence. It's not built to become your central store of personal data.
No new systems to adopt
We inspect your existing CRM, ERP, HRMS, cloud and website. You don't have to replace any of them.
Metadata, not datasets
Schema descriptions, settings and masked samples. Never full production tables.
Human expert on every material finding
MetricVibes DPDP experts validate results and co-own the fix plan.
Nothing is closed without proof
Each fix needs accepted evidence or a passing re-test before it counts as done.
How it works
From first audit to provable compliance
Onboard & map
Workspace, scope, team, and an inventory of systems, vendors and data flows.
Automated audit
34 DPDP controls checked against your questionnaire, inventory, evidence and connectors.
Expert review
A MetricVibes DPDP expert confirms, rejects or adjusts each finding, with reasons on record.
Fix
A remediation plan with owners, priorities and due dates, plus templates, APIs and engineering help.
Re-test
Controls are re-run on current data. A pass closes the finding; a fail reopens it with notes.
Prove & monitor
Dashboard, evidence library and management reports, kept current over time.
- Every result is one of five:
- Pass
- Warning
- Fail
- Review required
- Not applicable
Coverage
34 controls across 10 areas of the law
Each control carries a rule ID, DPDP reference, severity, evidence requirement, automation mode, business impact and remediation guidance. MetricVibes experts maintain and version the library as the regulations evolve.
Notice & transparency
Itemised, plain-language notice on every channel
s.5 · Rule 3Consent
Affirmative, granular, easy to withdraw, provable
s.6 · s.9 · Rule 10Data minimisation
Purpose for every system, field and data flow
s.4 · s.7Retention & deletion
Schedules, deletion jobs, 48-hour pre-erasure notice
s.8(7) · Rule 8Data principal rights
Intake, identity checks, SLA tracking
s.11–14 · Rule 14Grievance handling
Published contact, owner, resolution evidence
s.8(10) · s.13Processors & vendors
Contracts, DPAs, reviews, cross-border transfers
s.8(2) · s.16Security safeguards
Encryption, access control, 1-year logs, backups
s.8(5) · Rule 6Breach readiness
Incident plan, 72-hour Board report, user comms
s.8(6) · Rule 7Governance
Ownership, policy reviews, training, SDF duties
s.8(1) · s.10 · Rule 13The product
One place for leadership, and for the people doing the fixing
Screens shown use demo data from a fictional company.
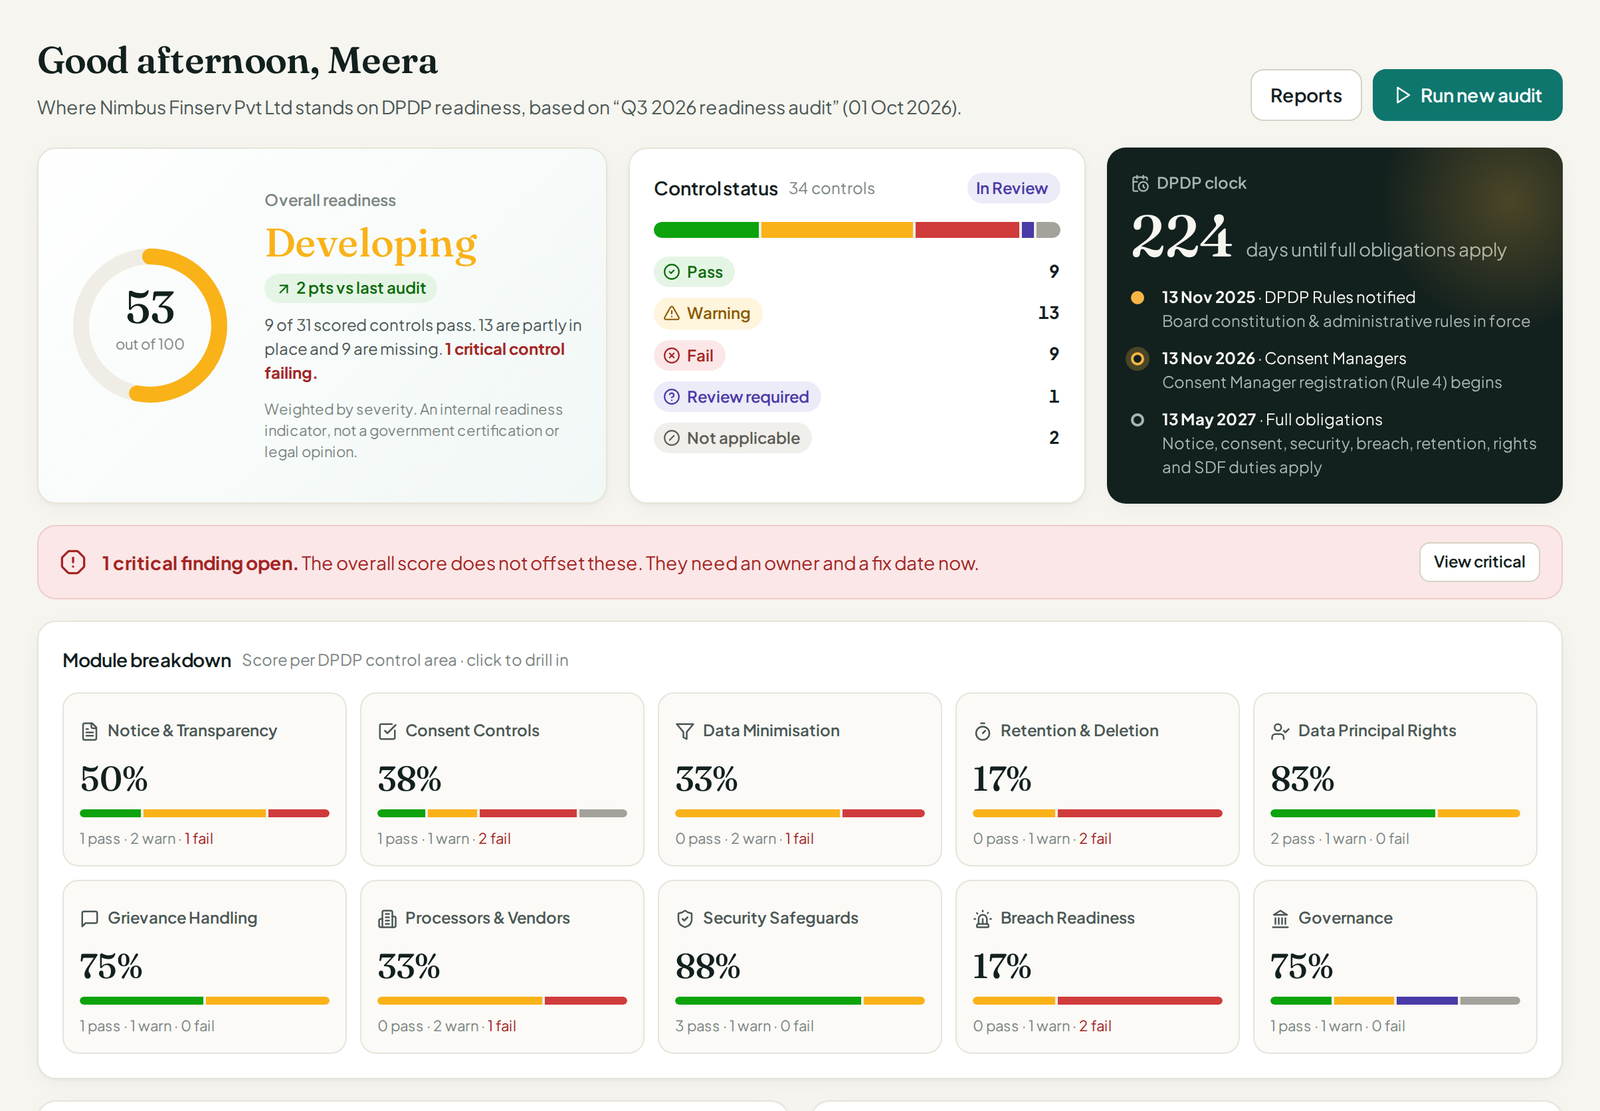
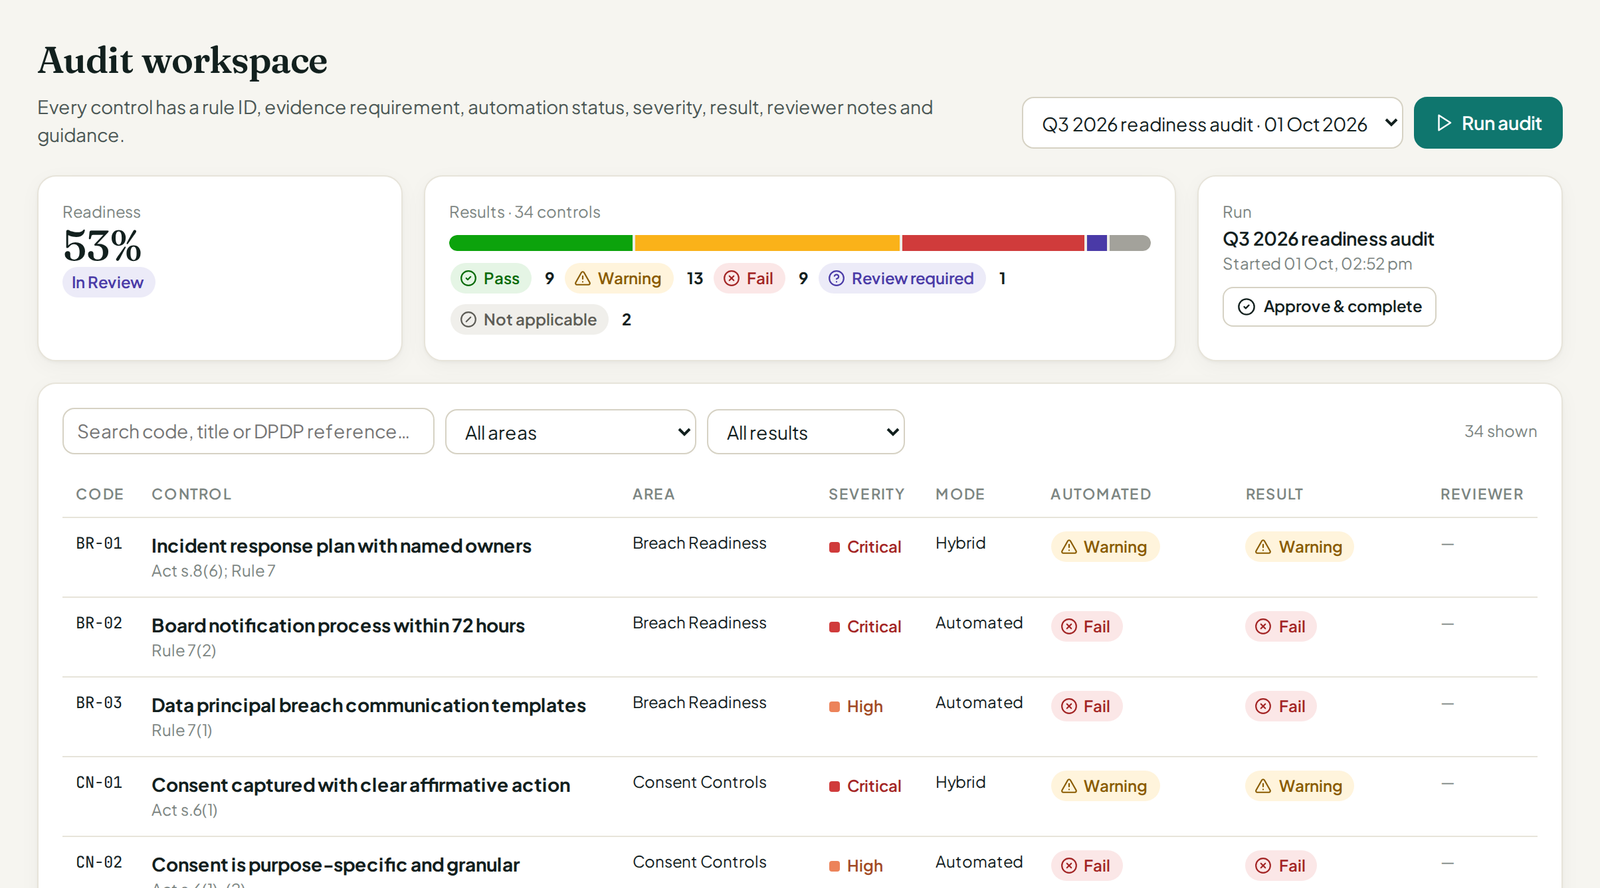
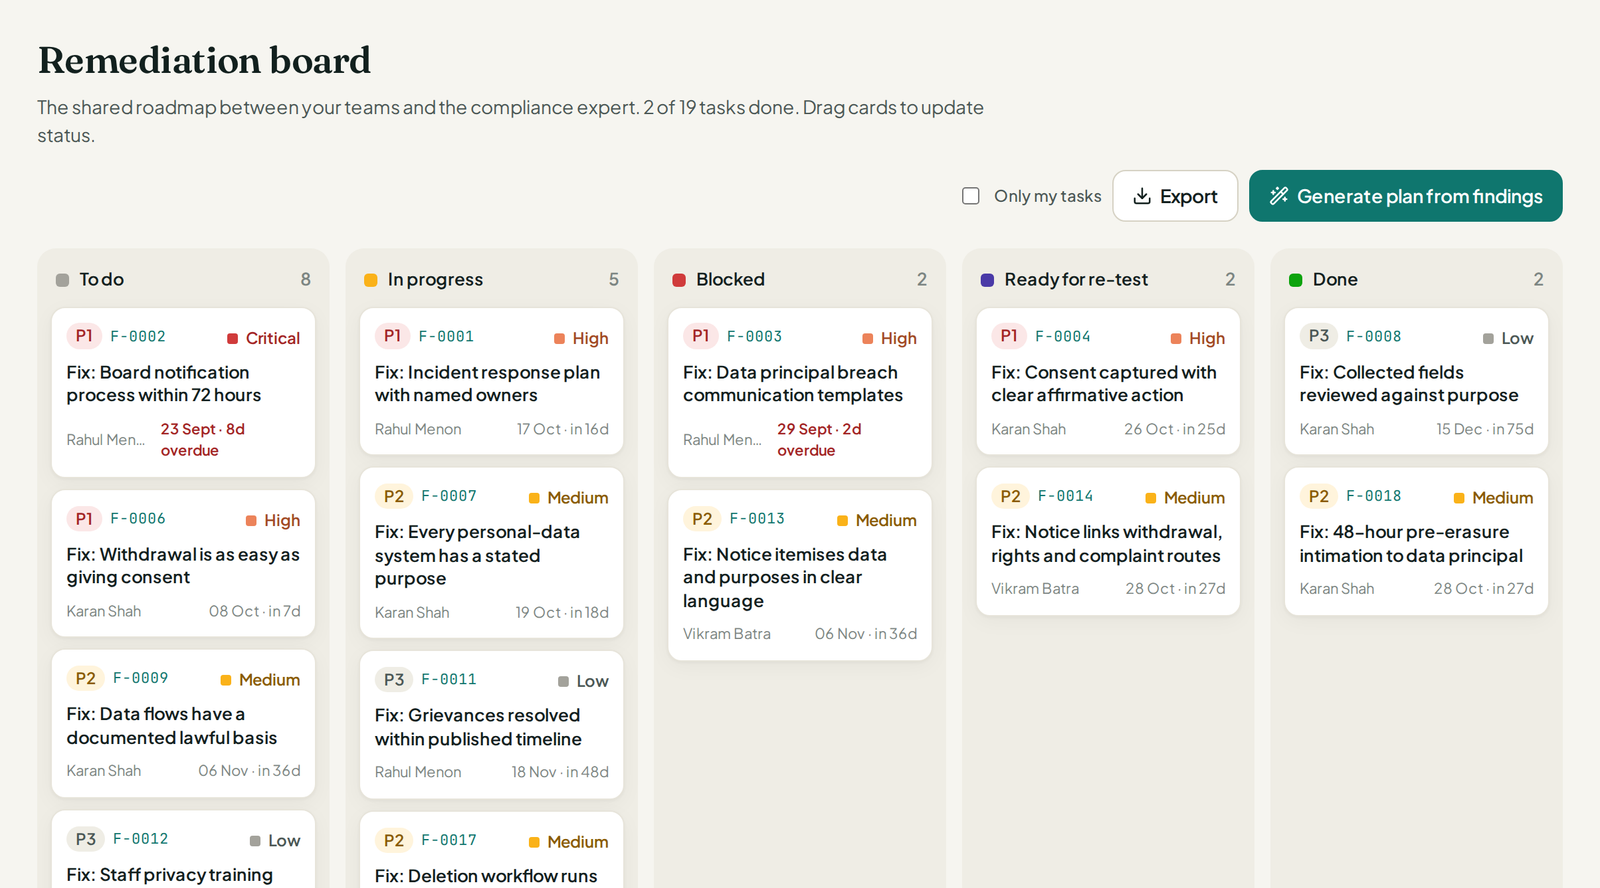
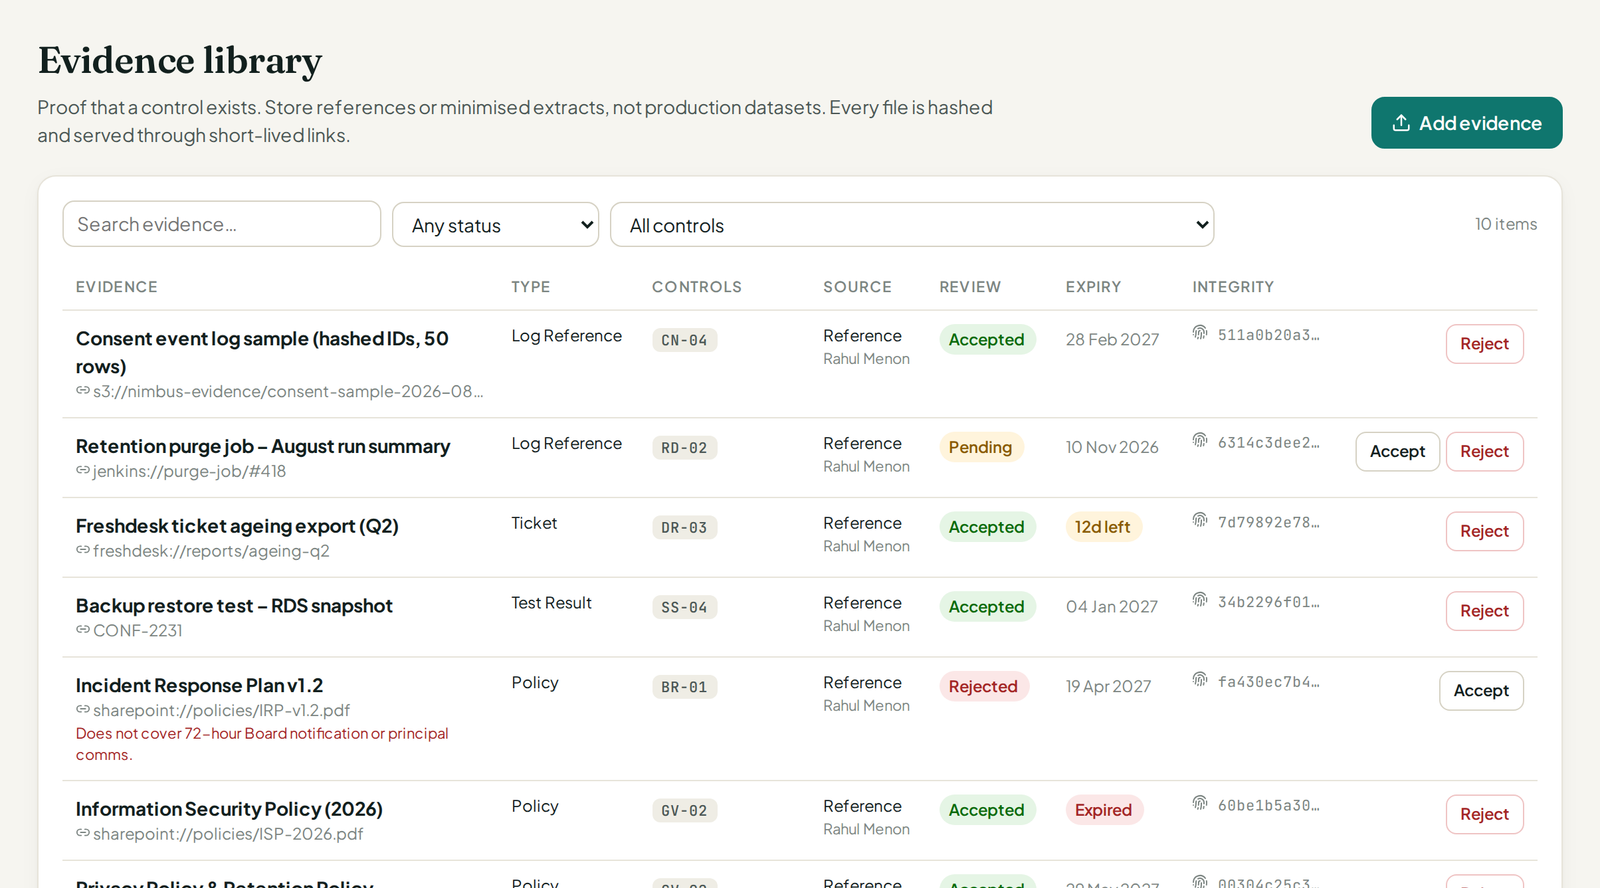
Human review is built in
Software finds the gaps. Experts decide what they mean
A named MetricVibes DPDP expert is assigned to your workspace. They review your setup, run clarification sessions with your teams and sign off on the remediation plan and reports.
Validate
Confirm, reject, edit or escalate each preliminary finding. Every decision carries a reason in the audit trail.
Clarify
Sessions with IT, legal, HR and marketing to cover the context software can't see.
Plan
Sequence, prioritise and assign fixes so they fit the way your business actually runs.
Approve
Review evidence and approve management reports before they're shared.
Secure by design
Built for BFSI and government scrutiny
Tenant isolation
Every record is scoped to your organisation on the server. Changing an ID or a URL can never expose another workspace.
Role-based access
Six roles, from Owner to Read-only Reviewer, with permissions enforced on every API call.
No raw credentials
Connectors use read-only, least-privilege scopes. Secrets stay in your vault; Praman only stores a reference to them.
Tamper-evident trail
The activity history is hash-chained, so any edit to past entries is detectable.
Evidence protection
File-type allow-list, SHA-256 hashing, short-lived signed download links and a malware-scanning hook.
Session security
Short-lived tokens, account lockout, rate limiting and the ability to revoke a user's sessions.
How we work together
From kickoff to continuous monitoring
What you need to start: a project owner, read access to your policies, and an hour each with IT, legal and the business units in scope. Connectors are optional; you can start with uploads and the questionnaire.
Onboard & map
Workspace setup, scope, team invites, system and vendor inventory, readiness questionnaire.
Audit & review
Automated audit, expert validation, clarification sessions, baseline report for leadership.
Remediate
Prioritised fixes with your teams: notices, consent, retention, vendors, breach playbooks.
Monitor & prove
Scheduled re-tests, evidence renewals, connector checks and quarterly reports.
Timelines are indicative and depend on scope and organisation size.
Get the Praman client deck
The full walkthrough as a PDF: the DPDP timeline, our approach, the 34 controls and how an engagement runs. Subscribe to the MetricVibes newsletter to unlock the download.
Start with a DPDP readiness baseline.
Within the first month you get a scored audit across all 10 areas, expert-validated findings and a prioritised fix plan.